

Key Takeaways
Attackers compromised Luxor's Commander platform and redirected an estimated 64,000 Bitcoin miners to the OCEAN mining pool.
The hijacked mining power reportedly reached 13.9 EH/s, with attackers receiving four payments totaling 0.324 BTC.
Luxor patched the vulnerability within two hours, promised full compensation to affected customers, and is strengthening its AI-powered cybersecurity defenses.
How Hackers Hijacked Luxor's Bitcoin Mining Operations
Luxor Technology has confirmed a security breach involving its Commander mining-management platform, after attackers redirected customers' Bitcoin mining power to the OCEAN mining pool. The incident has raised concerns about the security of Bitcoin mining operations and the growing use of artificial intelligence in cyberattacks.

Luxor on X
Luxor said that just over a dozen customer accounts were affected. While no official figure has been released for the number of mining machines impacted, some reports put the figure at approximately 64,000.
According to Luxor, the attack began around 6 PM Pacific time on November 14, 2026. Attackers gained unauthorized access to Commander, a platform that allows mining companies to monitor and manage large numbers of Bitcoin mining machines.
They used this access to change the mining pool settings of affected machines, redirecting their computing power to OCEAN.
Bitcoin miners use their machines to solve mathematical problems and help process transactions on the Bitcoin network. Many miners join mining pools, where they combine their computing power and share the rewards.
By changing the pool settings, attackers can redirect a machine's mining work to another pool. This means the machine's owner continues paying for electricity and running costs, while someone else may receive the mining rewards.
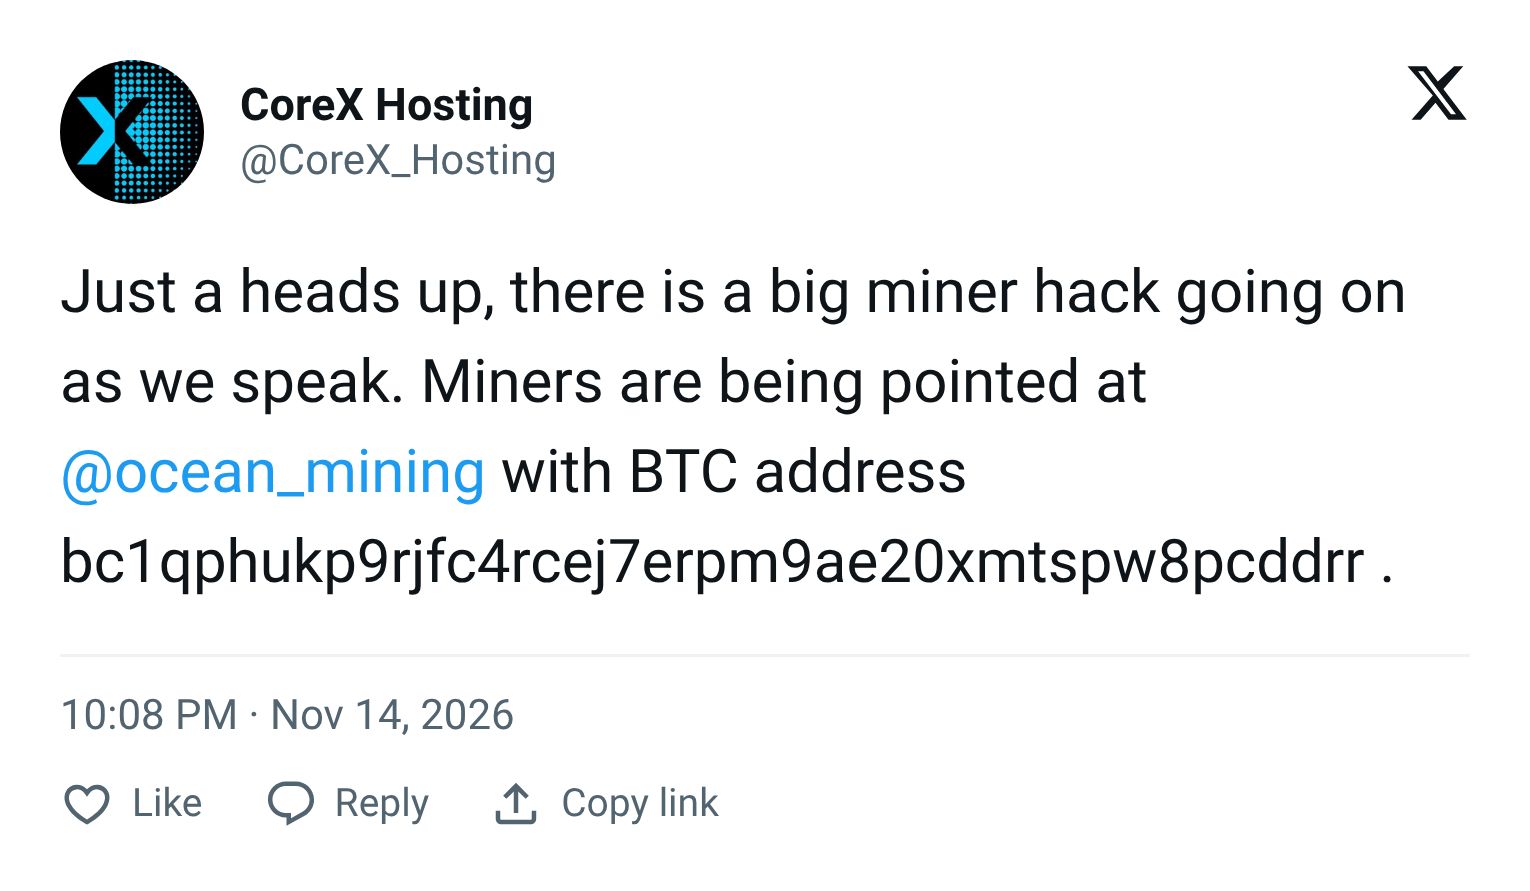
Infrastructure provider CoreX Hosting reported that around 13 EH/s of mining power was redirected to OCEAN. The sudden increase briefly pushed the pool's total hashrate close to 50 EH/s.
With Bitcoin's total network hashrate currently hovering around 900 EH/s, the stolen hashrate accounted for approximately 1.4% of the network's total computing power.
The attackers also reportedly replaced the legitimate Bitcoin payout addresses with an address they controlled. According to CoreX, hijacked miners are pointing to a specific address, bc1qphukp9rjfc4rcej7erpm9ae20xmtspw8pcddrr.
OCEAN's dashboard for that address shows that the hashrate associated with it briefly surged to 13.9 EH/s before plunging to 50 PH/s. The decline has continued since then, with the latest recorded hashrate standing at just 260 TH/s at the time of writing.
The hackers have received 4 payments from OCEAN at that address, totaling 0.324 BTC, according to mempool.space.

Under OCEAN's TIDES reward system, miners can still receive rewards for work submitted before disconnecting, provided the pool later finds a block. Therefore, the possibility of future payments to the suspected address could not be completely ruled out.
Luxor confirmed that its monitoring systems detected unauthorized changes to mining pool settings. Its engineering team responded immediately and patched the issue within two hours.
The company also began restoring affected machines to their original mining pool settings.
Luxor said the breach was limited to Commander and did not affect its other services, including Luxor Pool and LuxOS firmware. It also confirmed that no customer data was stolen or removed from its systems.
The company promised to fully compensate affected customers for the mining power redirected during the incident. "Every affected client will be paid in full for the redirected hashrate, as if it had mined normally," Luxor said in a statement.
CEO Nick Hansen also apologized to customers, acknowledging the seriousness of the breach. "You trust us with your fleet, and we need to be better," he wrote.
Luxor has promised to publish a detailed report explaining what happened and how the attackers gained access. The incident also prompted Hansen to warn that artificial intelligence is making cyberattacks more sophisticated and harder to defend against.
He described the attack as involving a "sophisticated AI-enabled vector." However, Luxor has not explained exactly how AI was used or published technical evidence showing how the attackers gained access.

Nick Hansen on X
In his post on X, Hansen warned that businesses, particularly those in the digital asset industry, are facing an increasing number of AI-assisted attacks. "At this moment, anyone running any sort of substantial business, especially in crypto, is inundated with AI-enabled attacks," he wrote.
He added that the situation is getting worse as AI models improve and more attackers begin using them.
Hansen also warned about so-called "abliterated" AI models. These are AI systems modified to remove many of their built-in safety restrictions, potentially making them easier to use for malicious activities such as developing hacking tools.
"Abliterated models are running 24/7 against your entire surface, looking for a little crack, which they then use to (almost instantly) expand," Hansen added.
To improve its defenses, Luxor has reportedly put most of its planned feature development on hold. The company has also acquired its own GPUs to run open-weight AI models for cybersecurity purposes.
The attack highlights an important security risk in the Bitcoin mining industry: the software used to manage mining machines can be just as important as the machines themselves.


